Other Articles
- IAM - Enable User MFA
- IAM - Enforce Key Rotation
- IAM - Enforce Active Key Limit
- IAM - Disable Unused User Credentials
- IAM - Enforce Group Permission
- IAM - Enforce Password Length
- IAM - Prohibit Password Reuse
- IAM - Check Root Access Keys Existence
- IAM - Enable Root MFA
- IAM - Establish Support Role
- IAM - Enable Key Rotation
- Purge Expired Certificates
- EC2 Volume – Enable EBS Volume Backup
- EC2 Volume – Enable EBS Encryption
- EFS – Enable EFS Storage Backup
- S3 Bucket – Enable S3 Bucket Versioning
- S3 Bucket – Enable S3 Bucket Encryption
- S3 Bucket – Block S3 Bucket Public Access
- RDS DB Instance – Encryption of Storage
- RDS DB Instance – Enable Deletion Protection
- RDS DB Instance – Enable Auto Minor Version Upgrade
- DynamoDB Table – Enable Table Encryption
- DynamoDB Table – Enable Table Point In Time Recovery
- DynamoDB Table – Enable Table Deletion Protection
- EKS Cluster – Enable Secrets Encryption
- OpenSearch Domain – Enable Encryption at Rest
- RDS DB Cluster – Retain Backups for 7 Days
- RDS DB Cluster – Encryption of Storage
- RDS DB Cluster – Enable Deletion Protection
- EC2 Instance – Monitor CPU Utilization
- ECS Service – Monitor CPU Utilization
- ECS Service – Monitor Memory Utilization
- RDS DB Instance – Monitor Free Storage Space
- RDS DB Instance – Monitor CPU Utilization
- SQS Queue – Monitor Message Age
- SQS Queue – Monitor Message Visibility
- DynamoDB Table – Monitor Table Read Capacity
- DynamoDB Table – Monitor Table Write Capacity
- DynamoDB Table – Monitor Table Latency
- Enable CloudTrail
- Encrypt CloudTrail Logs
- EC2 VPC – Ensure Flow Logs are Enabled
- EKS Cluster – Enable Control Plane Logging
- CloudWatch Log Group – Enable KMS Encryption
- CloudWatch Log Group – Configure Retention
- Load Balancer – Enable Access Logs
- RDS DB Instance – Block Public Access
- EC2 Security Group – Restrict Public SSH and RDP Access
- EC2 Security Group – Restrict Public Database Access
- EKS Cluster – Restrict Public Endpoint
- EC2 VPC – Restrict Default Security Group Traffic
- Load Balancer – Redirect HTTP Traffic to HTTPS
- Load Balancer – Use Strong TLS Policies
- OpenSearch Domain – Enable Node-to-Node Encryption
- OpenSearch Domain – Enforce HTTPS
- OpenSearch Domain – Restrict Public Access
- RDS DB Cluster – Block Public Access
- EC2 Instance – Enable Deletion Protection
- ECS Service – Enable Auto Scaling
- Load Balancer – Enable Deletion Protection
- Enable AWS Security Hub
- Enable GuardDuty
- CloudFront Distribution – Enforce HTTPS for Viewers
- CloudFront Distribution – Require TLS 1.2 for Viewers
- CloudFront Distribution – Associate a WAF Web ACL
- CloudFront Distribution – Protect S3 Origin Access
- KMS Key – Avoid Pending Deletion
- SNS Topic – Restrict Topic Policy Access
SNS Topic – Enable Encryption
Secure Configuration Checks > AWS
This check ensures that every Amazon SNS topic is encrypted at rest with an AWS KMS key. Encryption protects the messages that SNS stores while it delivers them.
Check Details
- Resource: SNS Topic
- Check: Enable SNS topic encryption (
EncryptionEnabled) - Risk: Sensitive messages are stored without a key you control
Key policy for AWS services
Add this statement to the policy of your customer managed key. Keep only the services that publish to the topic.
{
  "Sid": "AllowServicesToPublishToEncryptedTopic",
  "Effect": "Allow",
  "Principal": {
    "Service": [
      "cloudwatch.amazonaws.com",
      "events.amazonaws.com",
      "s3.amazonaws.com"
    ]
  },
  "Action": ["kms:GenerateDataKey*", "kms:Decrypt"],
  "Resource": "*"
}
Remediation via AWS Console
-
Log in to the AWS Management Console and open the Amazon SNS console.
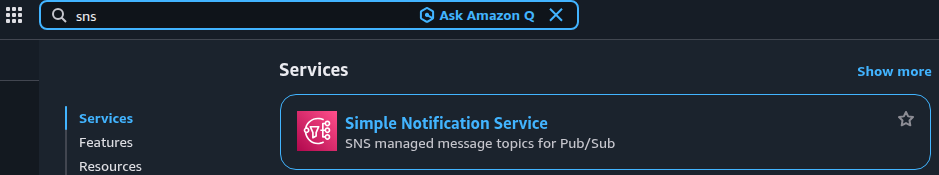
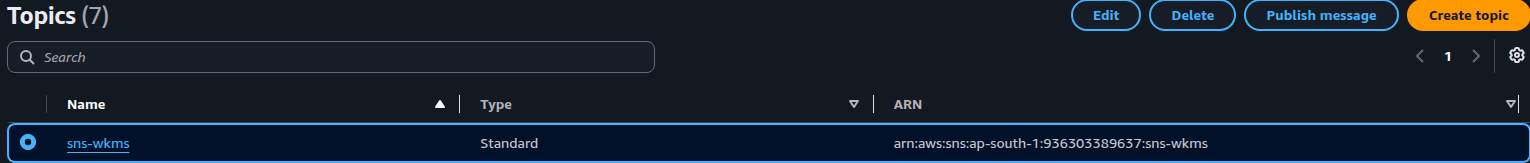
- In the left navigation pane, click Topics and select the affected topic.
-
Click Edit.
-
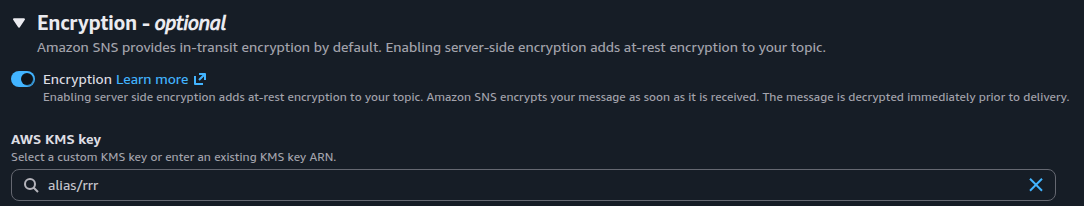
Expand Encryption and turn on Enable encryption. Choose an AWS managed key or a customer managed key.
- Click Save changes.
- Repeat steps 2 to 5 for every unencrypted topic.
Remediation via AWS CLI
-
Log in to the AWS Management Console and click the CloudShell icon (
>_) in the top-right corner.
-
List the topics that have no KMS key:
for ARN in $(aws sns list-topics \
  --query 'Topics[].TopicArn' --output text); do
  KEY=$(aws sns get-topic-attributes \
    --topic-arn "$ARN" \
    --query 'Attributes.KmsMasterKeyId' \
    --output text)
  if [ "$KEY" = "None" ]; then echo "$ARN"; fi
done
The command covers one region. Add
--region <region>to each command to check another. -
Enable encryption on a topic:
aws sns set-topic-attributes \
--topic-arn <topic-arn> \
--attribute-name KmsMasterKeyId \
--attribute-value <kms-key>
-
Verify the key on the topic:
aws sns get-topic-attributes \
--topic-arn <topic-arn> \
--query 'Attributes.KmsMasterKeyId'
Replace <topic-arn> with the topic ARN, for example arn:aws:sns:us-east-1:123456789012:my-topic.
Replace <kms-key> with alias/aws/sns, or with the ID, ARN or alias of your own key.
Updated on 04 November, 2026