Other Articles
- IAM - Enable User MFA
- IAM - Enforce Key Rotation
- IAM - Enforce Active Key Limit
- IAM - Disable Unused User Credentials
- IAM - Enforce Group Permission
- IAM - Enforce Password Length
- IAM - Prohibit Password Reuse
- IAM - Check Root Access Keys Existence
- IAM - Enable Root MFA
- IAM - Establish Support Role
- IAM - Enable Key Rotation
- Purge Expired Certificates
- EC2 Volume – Enable EBS Volume Backup
- EC2 Volume – Enable EBS Encryption
- EFS – Enable EFS Storage Backup
- S3 Bucket – Enable S3 Bucket Versioning
- S3 Bucket – Enable S3 Bucket Encryption
- S3 Bucket – Block S3 Bucket Public Access
- RDS DB Instance – Encryption of Storage
- RDS DB Instance – Enable Deletion Protection
- RDS DB Instance – Enable Auto Minor Version Upgrade
- DynamoDB Table – Enable Table Encryption
- DynamoDB Table – Enable Table Point In Time Recovery
- DynamoDB Table – Enable Table Deletion Protection
- EKS Cluster – Enable Secrets Encryption
- OpenSearch Domain – Enable Encryption at Rest
- RDS DB Cluster – Retain Backups for 7 Days
- RDS DB Cluster – Encryption of Storage
- RDS DB Cluster – Enable Deletion Protection
- EC2 Instance – Monitor CPU Utilization
- ECS Service – Monitor CPU Utilization
- ECS Service – Monitor Memory Utilization
- RDS DB Instance – Monitor Free Storage Space
- RDS DB Instance – Monitor CPU Utilization
- SQS Queue – Monitor Message Age
- SQS Queue – Monitor Message Visibility
- DynamoDB Table – Monitor Table Read Capacity
- DynamoDB Table – Monitor Table Write Capacity
- DynamoDB Table – Monitor Table Latency
- Enable CloudTrail
- Encrypt CloudTrail Logs
- EC2 VPC – Ensure Flow Logs are Enabled
- EKS Cluster – Enable Control Plane Logging
- CloudWatch Log Group – Enable KMS Encryption
- CloudWatch Log Group – Configure Retention
- Load Balancer – Enable Access Logs
- RDS DB Instance – Block Public Access
- EC2 Security Group – Restrict Public SSH and RDP Access
- EC2 Security Group – Restrict Public Database Access
- EC2 VPC – Restrict Default Security Group Traffic
- Load Balancer – Redirect HTTP Traffic to HTTPS
- Load Balancer – Use Strong TLS Policies
- OpenSearch Domain – Enable Node-to-Node Encryption
- OpenSearch Domain – Enforce HTTPS
- OpenSearch Domain – Restrict Public Access
- RDS DB Cluster – Block Public Access
- EC2 Instance – Enable Deletion Protection
- ECS Service – Enable Auto Scaling
- Load Balancer – Enable Deletion Protection
- Enable AWS Security Hub
- Enable GuardDuty
- CloudFront Distribution – Enforce HTTPS for Viewers
- CloudFront Distribution – Require TLS 1.2 for Viewers
- CloudFront Distribution – Associate a WAF Web ACL
- CloudFront Distribution – Protect S3 Origin Access
- KMS Key – Avoid Pending Deletion
- SNS Topic – Enable Encryption
- SNS Topic – Restrict Topic Policy Access
EKS Cluster – Restrict Public Endpoint
Secure Configuration Checks > AWS
This check ensures that the API server endpoint of an Amazon EKS cluster is private or limited to specific CIDR ranges. By default, the endpoint is reachable from the entire internet. Anyone can then try to reach the Kubernetes API and attack it.
Check Details
- Resource: EKS Cluster
- Check: Restrict EKS cluster public endpoint (
PublicEndpointRestricted) - Risk: Attackers can probe the Kubernetes API, guess or abuse credentials, and take control of the cluster and its workloads
Endpoint access modes
- Public: The endpoint is reachable from the internet. It is compliant only if you limit it to trusted CIDR ranges.
- Public and private: The endpoint is reachable from the internet and from inside the VPC. It is compliant only if you limit the public CIDRs. Worker nodes use the private path.
- Private: The endpoint is reachable only from inside the VPC or from networks connected to it. This is the safest mode.
Remediation via AWS Console
-
Log in to the AWS Management Console and open the Amazon Elastic Kubernetes Service (EKS) console.
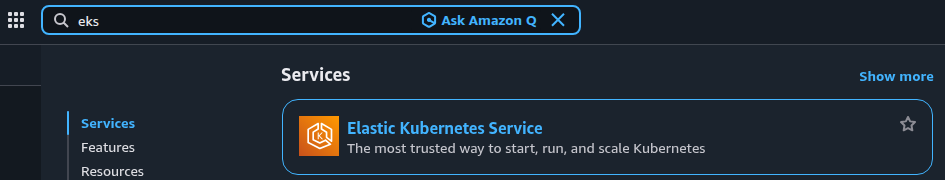
-
In the left navigation pane, select Clusters and choose the affected cluster.
-
Open the Configuration tab. Under the Networking section, click Endpoint access.
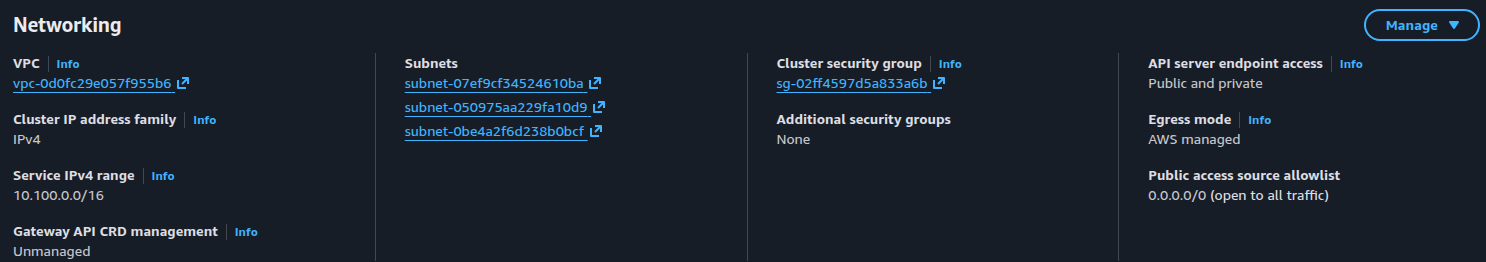
-
Configure the cluster API server endpoint access using one of the following options:
- Private access only: Enable Private access and disable Public access to prevent access to the Kubernetes API server from the public internet.
-
Public and private access: Enable both Public access and Private access. Under Advanced settings, specify trusted CIDR ranges and remove unrestricted access such as
0.0.0.0/0and::/0, where applicable.
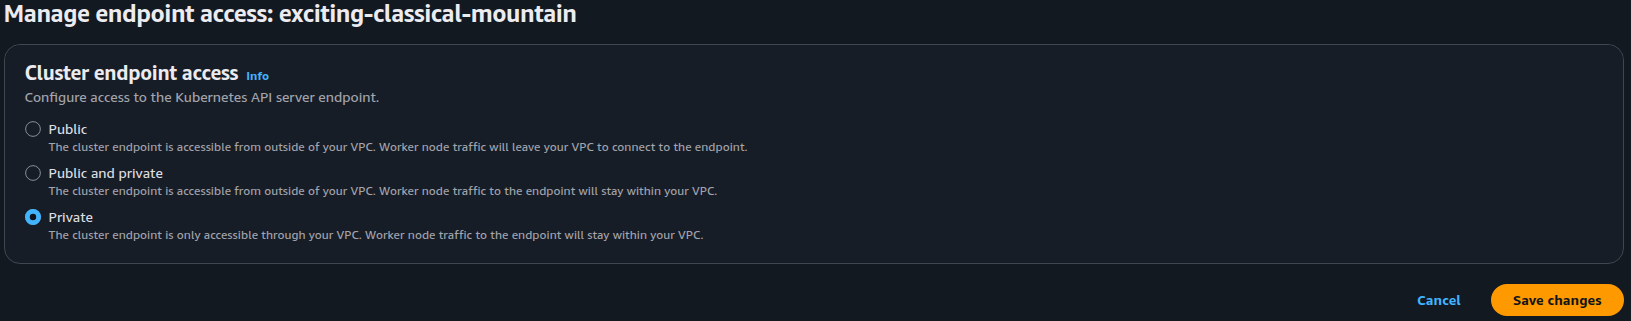
-
Click Update to apply the endpoint access configuration.
-
Wait for the endpoint access update to complete. Check the cluster's Updates tab and verify that the update status is Successful.
-
Repeat these steps for every affected EKS cluster.
Note: Before disabling public access, ensure that administrators, CI/CD pipelines, and other management tools can access the private Kubernetes API endpoint through the cluster VPC or a connected network. If public access is retained, allow only trusted CIDR ranges. When restricting public access, ensure that the required NAT Gateway or other egress IP addresses used by worker nodes are included in the allowlist if private endpoint access is disabled.
Remediation via AWS CLI
-
Log in to the AWS Management Console and click the CloudShell icon (
>_) in the top-right corner.
-
List the clusters whose public endpoint is open to the internet:
for c in $(aws eks list-clusters --query 'clusters[]' --output text); do
  aws eks describe-cluster --name "$c" --output json | \
  jq -r '.cluster
    | select(.resourcesVpcConfig.endpointPublicAccess == true
        and (.resourcesVpcConfig.publicAccessCidrs
             | any(.[]; . == "0.0.0.0/0" or . == "::/0")))
    | .name'
done
The command covers one region. Add
--region <region>to eachawscommand to check another. -
Limit public access to trusted CIDR ranges and keep private access on:
aws eks update-cluster-config \
--name <cluster-name> \
--resources-vpc-config '{"endpointPublicAccess":true,"endpointPrivateAccess":true,"publicAccessCidrs":["<trusted-cidr-1>","<trusted-cidr-2>"]}'
To remove public access completely, use this command instead:
aws eks update-cluster-config \
--name <cluster-name> \
--resources-vpc-config endpointPublicAccess=false,endpointPrivateAccess=true
-
Wait for the update to finish:
aws eks wait cluster-active --name <cluster-name>
-
Verify the endpoint settings:
aws eks describe-cluster \
--name <cluster-name> \
--query 'cluster.resourcesVpcConfig.{Public:endpointPublicAccess,Private:endpointPrivateAccess,Cidrs:publicAccessCidrs}'
Replace <cluster-name> with the name of the cluster, for example prod-cluster.
Replace <trusted-cidr-1> and <trusted-cidr-2> with your own ranges, for example 203.0.113.0/24.
Repeat steps 3 to 5 for each cluster.
Updated on 03 November, 2026