Other Articles
- IAM - Enable User MFA
- IAM - Enforce Key Rotation
- IAM - Enforce Active Key Limit
- IAM - Disable Unused User Credentials
- IAM - Enforce Group Permission
- IAM - Enforce Password Length
- IAM - Prohibit Password Reuse
- IAM - Check Root Access Keys Existence
- IAM - Enable Root MFA
- IAM - Establish Support Role
- IAM - Enable Key Rotation
- Purge Expired Certificates
- EC2 Volume – Enable EBS Volume Backup
- EC2 Volume – Enable EBS Encryption
- EFS – Enable EFS Storage Backup
- S3 Bucket – Enable S3 Bucket Versioning
- S3 Bucket – Enable S3 Bucket Encryption
- S3 Bucket – Block S3 Bucket Public Access
- RDS DB Instance – Encryption of Storage
- RDS DB Instance – Enable Deletion Protection
- RDS DB Instance – Enable Auto Minor Version Upgrade
- DynamoDB Table – Enable Table Encryption
- DynamoDB Table – Enable Table Point In Time Recovery
- DynamoDB Table – Enable Table Deletion Protection
- EKS Cluster – Enable Secrets Encryption
- OpenSearch Domain – Enable Encryption at Rest
- RDS DB Cluster – Retain Backups for 7 Days
- RDS DB Cluster – Encryption of Storage
- RDS DB Cluster – Enable Deletion Protection
- EC2 Instance – Monitor CPU Utilization
- ECS Service – Monitor CPU Utilization
- ECS Service – Monitor Memory Utilization
- RDS DB Instance – Monitor Free Storage Space
- RDS DB Instance – Monitor CPU Utilization
- SQS Queue – Monitor Message Age
- SQS Queue – Monitor Message Visibility
- DynamoDB Table – Monitor Table Read Capacity
- DynamoDB Table – Monitor Table Write Capacity
- DynamoDB Table – Monitor Table Latency
- Enable CloudTrail
- Encrypt CloudTrail Logs
- EC2 VPC – Ensure Flow Logs are Enabled
- EKS Cluster – Enable Control Plane Logging
- CloudWatch Log Group – Enable KMS Encryption
- CloudWatch Log Group – Configure Retention
- Load Balancer – Enable Access Logs
- RDS DB Instance – Block Public Access
- EC2 Security Group – Restrict Public SSH and RDP Access
- EC2 Security Group – Restrict Public Database Access
- EKS Cluster – Restrict Public Endpoint
- EC2 VPC – Restrict Default Security Group Traffic
- Load Balancer – Redirect HTTP Traffic to HTTPS
- Load Balancer – Use Strong TLS Policies
- OpenSearch Domain – Enable Node-to-Node Encryption
- OpenSearch Domain – Enforce HTTPS
- OpenSearch Domain – Restrict Public Access
- EC2 Instance – Enable Deletion Protection
- ECS Service – Enable Auto Scaling
- Load Balancer – Enable Deletion Protection
- Enable AWS Security Hub
- Enable GuardDuty
- CloudFront Distribution – Enforce HTTPS for Viewers
- CloudFront Distribution – Require TLS 1.2 for Viewers
- CloudFront Distribution – Associate a WAF Web ACL
- CloudFront Distribution – Protect S3 Origin Access
- KMS Key – Avoid Pending Deletion
- SNS Topic – Enable Encryption
- SNS Topic – Restrict Topic Policy Access
RDS DB Cluster – Block Public Access
Secure Configuration Checks > AWS
This check ensures that Amazon RDS clusters are not publicly accessible. For Aurora, every instance in the cluster must also be private.
Check Details
- Resource: RDS DB Cluster
- Check: Block public access to RDS cluster (
BlockPublicAccess) - Risk: The database endpoint can be reached from the internet
Remediation via AWS Console
-
Open the Amazon RDS console.
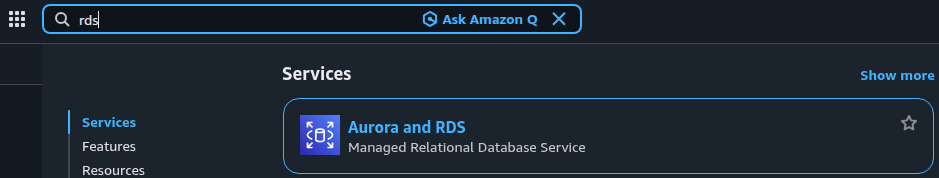
-
Go to Databases and select the affected DB instance. For Aurora, select each instance in the cluster.
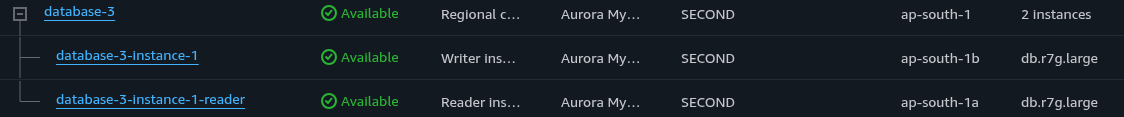
-
Click Modify.
-
Under Connectivity, expand Additional configuration and set Publicly accessible to No.
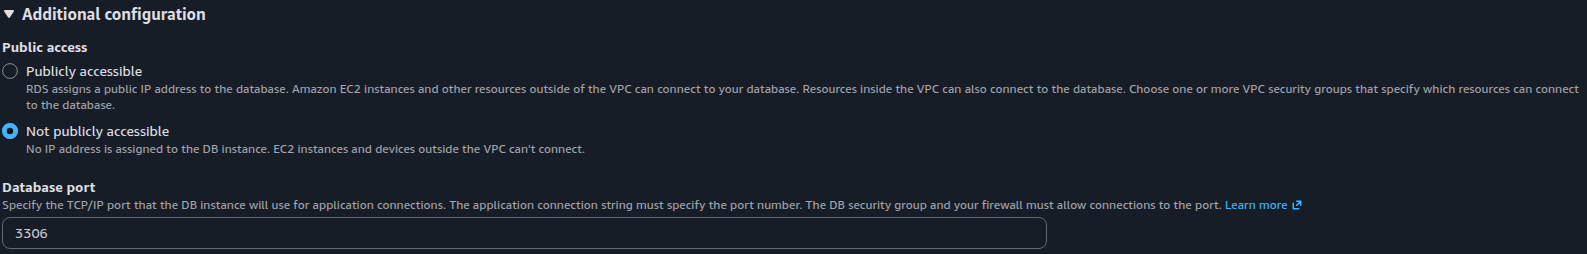
-
Click Continue, select Apply immediately if appropriate, and click Modify DB instance.
-
Repeat for every affected DB instance.
Note: For existing Multi-AZ DB clusters, the Public access setting cannot be modified through the cluster modification workflow. Review the deployment and network configuration separately.
Remediation via AWS CLI
-
Log in to the AWS Management Console and click the CloudShell icon (
>_) in the top-right corner.
-
List the public instances that belong to a cluster (Aurora):
aws rds describe-db-instances \
--query 'DBInstances[?PubliclyAccessible && DBClusterIdentifier].[DBInstanceIdentifier,DBClusterIdentifier,Engine]' \
--output table
List the public Multi-AZ DB clusters:
aws rds describe-db-clusters \
--query 'DBClusters[?PubliclyAccessible].[DBClusterIdentifier,Engine]' \
--output table
The commands cover one region. Add
--region <region>to check another. -
Make an Aurora instance private. Repeat for every instance from the first list:
aws rds modify-db-instance \
--db-instance-identifier <instance-id> \
--no-publicly-accessible \
--apply-immediately
-
Make a Multi-AZ DB cluster private:
aws rds modify-db-cluster \
--db-cluster-identifier <cluster-id> \
--no-publicly-accessible \
--apply-immediately
-
Verify the setting. For Aurora, check every instance:
aws rds describe-db-instances \
--query 'DBInstances[?DBClusterIdentifier==`<cluster-id>`].[DBInstanceIdentifier,PubliclyAccessible]' \
--output table
Replace <instance-id> with the instance name, for example my-aurora-instance-1.
Replace <cluster-id> with the cluster name, for example my-aurora-cluster.
For a Multi-AZ DB cluster, verify with aws rds describe-db-clusters and look at PubliclyAccessible.
Updated on 05 November, 2026