Other Articles
- Cloud SQL – Configure Private IP
- Cloud SQL – Monitor CPU Utilization
- Cloud SQL – Enable Deletion Protection
- Cloud SQL – Enable Disk Encryption
- Cloud SQL – Enable Automated Backups
- Cloud SQL – Enable Log Export
- Cloud SQL – Enforce Password Validation
- Cloud SQL – Protect From Internet Access
- Cloud SQL – Enforce Secure Transport
- Compute Engine – Block Project-Wide SSH Keys
- Compute Engine – Disable IP Forwarding
- Compute Engine – Disable Public IP Addresses
- Compute Engine – Disable Serial Port Access
- Compute Engine – Enable Confidential Computing
- Compute Engine – Enable OS Login
- Compute Engine – Enable Shielded VM
- Compute Engine – Restrict Default Service Account
- General – Deny Public Access to KMS Keys
- General – Enforce Duties Separation
- General – Enforce KMS Key Rotation
- General – Restrict Admin Roles on Service Accounts
- Cloud Run – Configure Timeout Settings
- Cloud Storage – Enable Bucket Encryption
- Cloud Storage – Enable Bucket Logging
- Cloud Storage – Enable Bucket Versioning
- Cloud Storage – Enforce Uniform Bucket-Level Access
- Cloud Storage – Restrict Public Access
- IAM Users – Enforce GCP-Managed Keys
- IAM Users – Rotate External User-Managed Service Account Keys
- GKE – Enable Private Nodes
- GKE – Restrict Control Plane Access
- GKE – Enable Workload Identity
- GKE – Disable Legacy ABAC
- GKE – Enable Network Policy
- GKE – Enable Shielded Nodes
- GKE – Enable Node Auto-Upgrade and Auto-Repair
- GKE Cluster – Enable Cluster Logging
- General – Enable Cloud Audit Logs
- General – Configure a Log Sink
- General – Configure Log Bucket Retention
- Cloud SQL – Enable High Availability
- Cloud SQL – Configure Maintenance Window
- Cloud Storage – Configure Bucket Retention or Lifecycle
- General – Enable Security Command Center
- Compute Engine – Enable Instance Deletion Protection
- VPC Firewall – Restrict Public SSH and RDP Access
- VPC Firewall – Restrict Public Database Access
- VPC Network – Enable Subnet Flow Logs
VPC Network – Avoid the Default Network
Secure Configuration Checks > GCP
This check ensures that the default VPC network does not exist in the project. Use custom networks that you design and secure yourself.
Check Details
- Resource: VPC Network
- Check: Avoid the default network
- Risk: The default network has a subnet in every region and permissive firewall rules. This widens the attack surface and makes it easy to expose resources by mistake.
Remediation via Google Cloud Console
-
Log in to the Google Cloud Console and navigate to
VPC network > VPC networks.

-
Click Create VPC network. Enter a network name and set
Subnet creation mode to Custom.
Configure a subnet by providing its name, region and IP range, then click
Create.
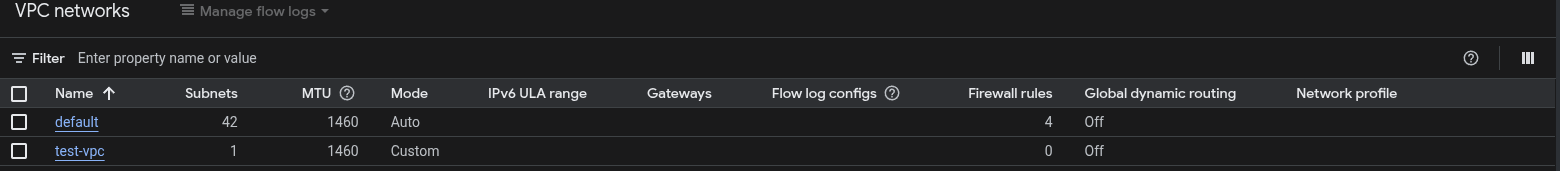
-
Recreate or migrate the resources using the
defaultnetwork to the new custom network. Update their network configurations and connectivity as required. -
Return to VPC network > VPC networks
and select the
defaultnetwork. -
Click Delete VPC network and confirm the deletion.

-
Verify that the
defaultnetwork no longer appears in the VPC networks list.
Remediation via Google Cloud CLI
-
Open the Google Cloud Console and launch
Cloud Shell.
-
Check whether the default network exists:
gcloud compute networks list --filter="name=default"
-
Create a custom network and a subnet:
gcloud compute networks create <NETWORK_NAME> --subnet-mode=custom

gcloud compute networks subnets create <SUBNET_NAME> \
--network=<NETWORK_NAME> \
--region=<REGION> \
--range=<IP_RANGE>
Replace the values with your own names, for example
us-central1for the region and10.0.0.0/24for the range. Then move or recreate the resources that use the default network in the new network. -
Delete the firewall rules of the default network:
gcloud compute firewall-rules list \
--filter='network~"/default$"' \
--format="value(name)" | \
xargs -r gcloud compute firewall-rules delete --quiet
-
Delete the default network:
gcloud compute networks delete default
The command fails if resources still use the network. Move them first.
-
Verify that the default network is gone:
gcloud compute networks list --filter="name=default"
The command must list no networks.

Default Value
By default, new projects get a default network.
An organization policy can stop this.
Use the compute.skipDefaultNetworkCreation constraint.
Updated on 09 November, 2026